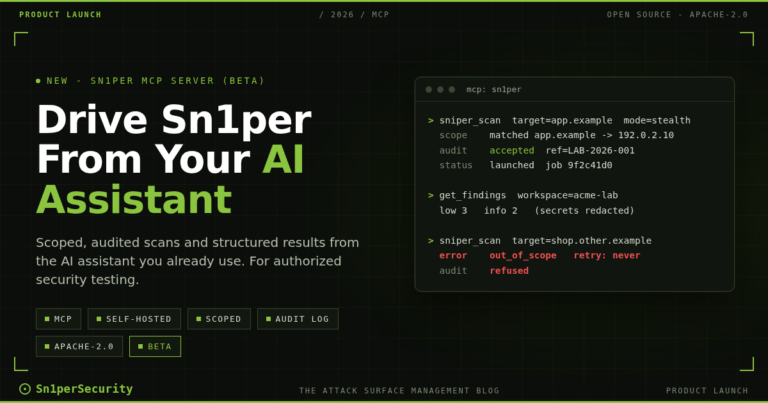
Sn1per Scan Engine v11.1 brings agentic AI pentesting into the scan: AI triage of tool output, adaptive tool selection, five AI vulnerability specialists with…
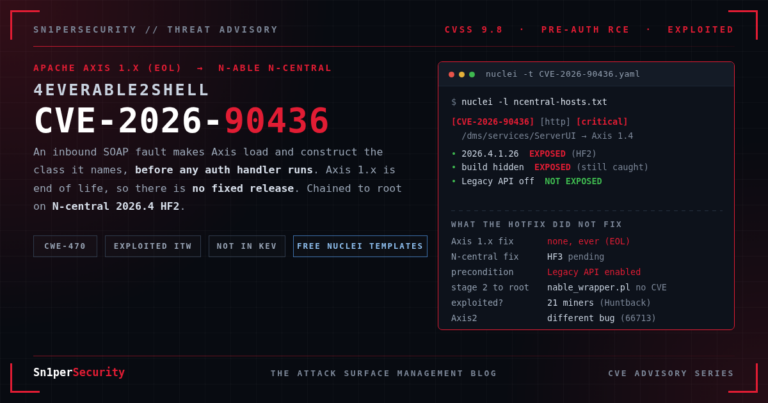
CVE-2026-90436 lets an unauthenticated attacker make Apache Axis 1.x load and instantiate a Java class named in an inbound SOAP fault, before any authentication…
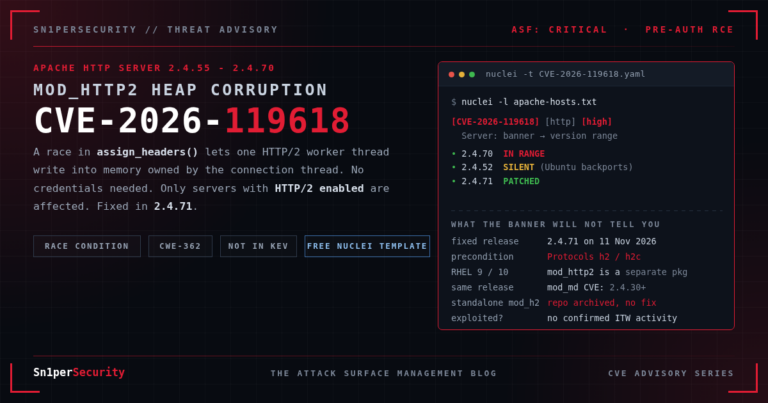
CVE-2026-119618 is a race condition in Apache mod_http2 that corrupts the heap and can lead to unauthenticated remote code execution. It affects httpd 2.4.55…
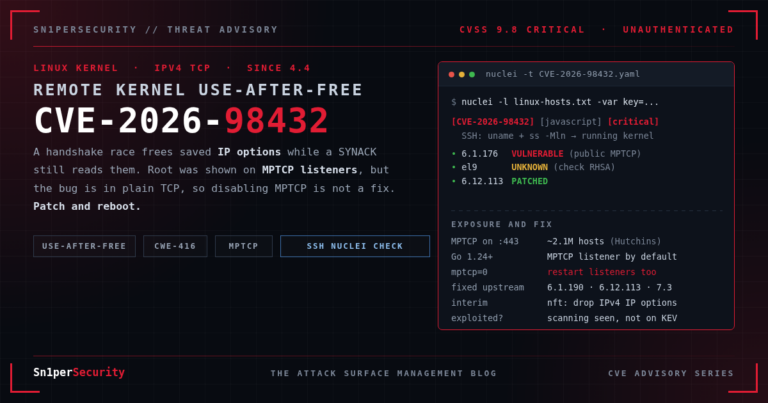
CVE-2026-98432 is a CVSS 9.8 use-after-free in the Linux kernel's IPv4 TCP handshake, present since Linux 4.4. Remote root has been demonstrated against servers…
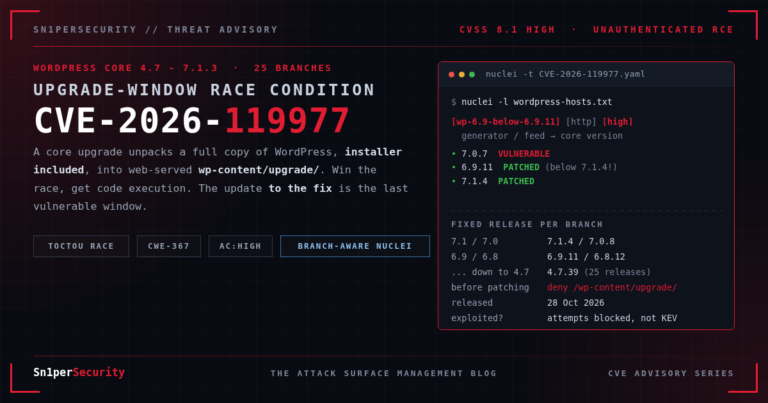
CVE-2026-119977 lets an unauthenticated attacker race a WordPress core upgrade to remote code execution through the staged copy WordPress unpacks under wp-content/upgrade/. WordPress 7.1.4…
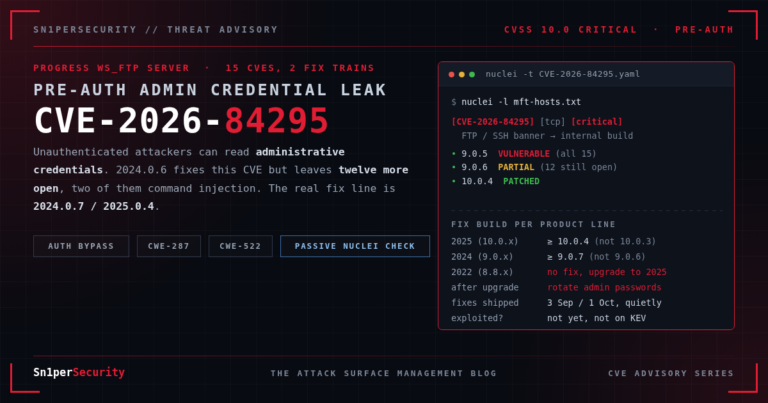
CVE-2026-84295 is a CVSS 10.0 pre-auth Progress WS_FTP Server vulnerability that discloses administrative credentials. It is fixed in 2024.0.6 and 2025.0.3, but twelve more…
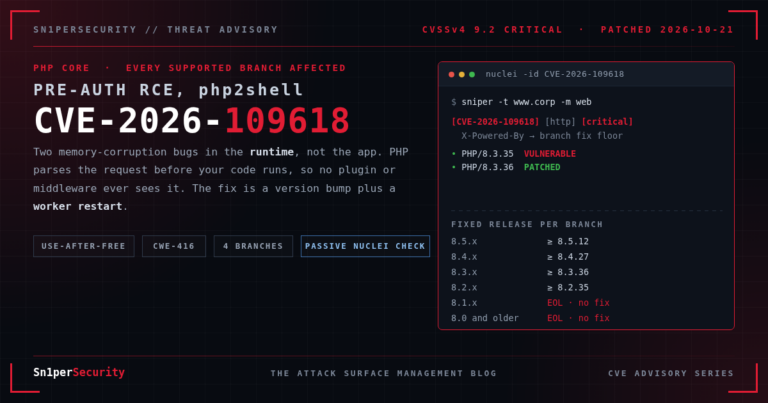
CVE-2026-109618 and CVE-2026-109619 are two CVSS 9.2 pre-auth remote code execution flaws in PHP core, patched 21 October 2026. Get the passive four-branch Nuclei…
 Attack Surface Management
 xer0dayz
·
23 min read