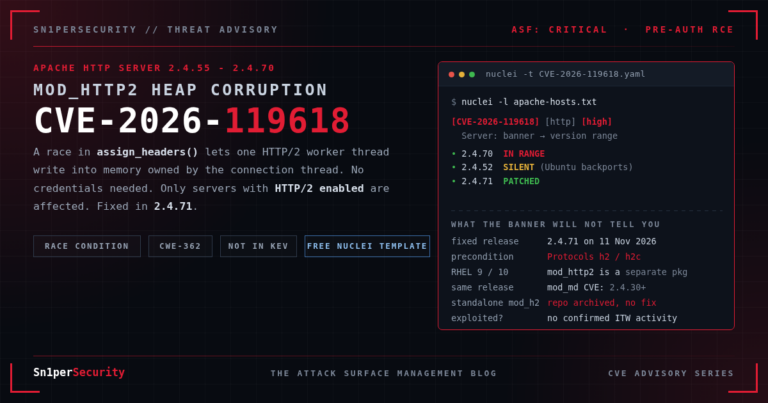
CVE-2026-119618 is a race condition in Apache mod_http2 that corrupts the heap and can lead to unauthenticated remote code execution. It affects httpd 2.4.55…
CVE-2026-98432 is a CVSS 9.8 use-after-free in the Linux kernel's IPv4 TCP handshake, present since Linux 4.4. Remote root has been demonstrated against servers…
CVE-2026-119977 lets an unauthenticated attacker race a WordPress core upgrade to remote code execution through the staged copy WordPress unpacks under wp-content/upgrade/. WordPress 7.1.4…
CVE-2026-84295 is a CVSS 10.0 pre-auth Progress WS_FTP Server vulnerability that discloses administrative credentials. It is fixed in 2024.0.6 and 2025.0.3, but twelve more…
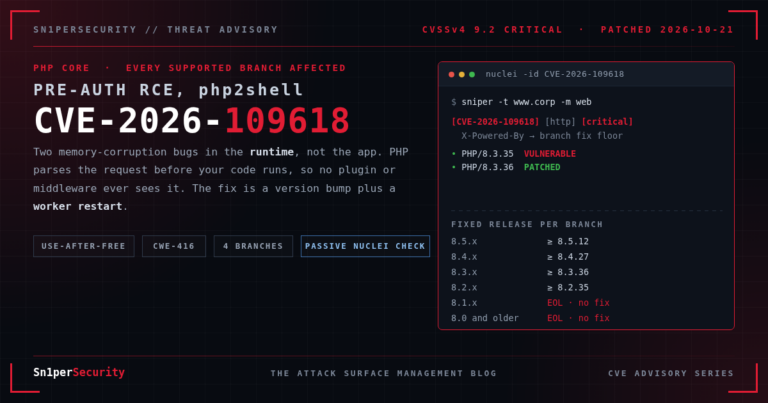
CVE-2026-109618 and CVE-2026-109619 are two CVSS 9.2 pre-auth remote code execution flaws in PHP core, patched 21 October 2026. Get the passive four-branch Nuclei…
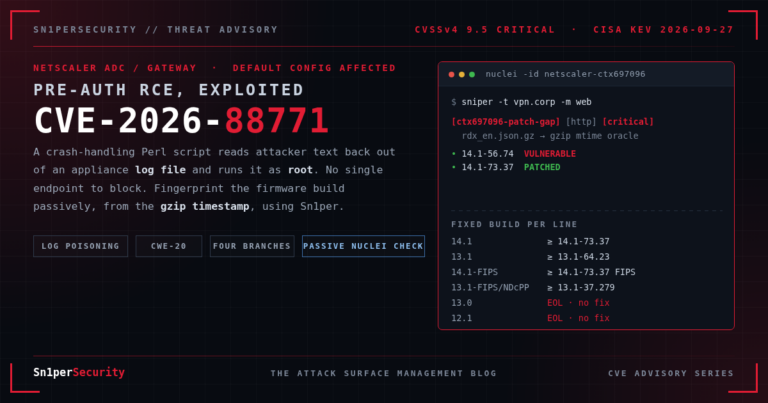
CVE-2026-88771 and CVE-2026-88772 are actively exploited Citrix NetScaler RCE zero-days in CISA KEV. Get the passive Nuclei template, the four-branch patch-gap logic, and how…
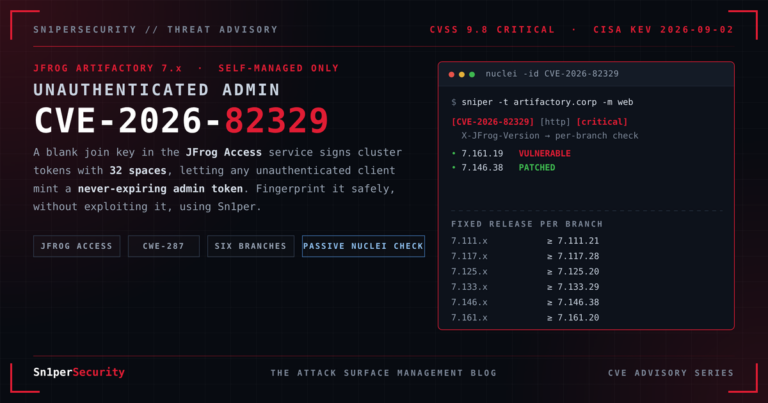
CVE-2026-82329 is a critical, unauthenticated JFrog Artifactory authentication bypass in CISA KEV. Get the passive Nuclei template, the six-branch version logic, and how to…
CVE-2026-9082 is an actively exploited, unauthenticated SQL injection in Drupal core on PostgreSQL. Learn how to detect every affected host with Sn1per and Nuclei.
xer0dayz·7 min read
Try it free
See your attack surface like a pentester would.
Sn1per finds, ranks, and exploits real vulnerabilities autonomously - the same way attackers do.
 Attack Surface Management
 xer0dayz
·
19 min read